access.yml.
This keeps responsibility split cleanly:
Define roles
Commitaccess.yml at the project root:
stb compile rejects unknown roles, pipelines, permissions, keys, and invalid scopes. The built-in
admin and viewer roles cannot be redefined. Account management and role assignment remain
system-administrator operations and cannot be granted in this file.
Choose a scope
Each grant contains exactly one scope:
The permission vocabulary is intentionally closed:
Assign roles
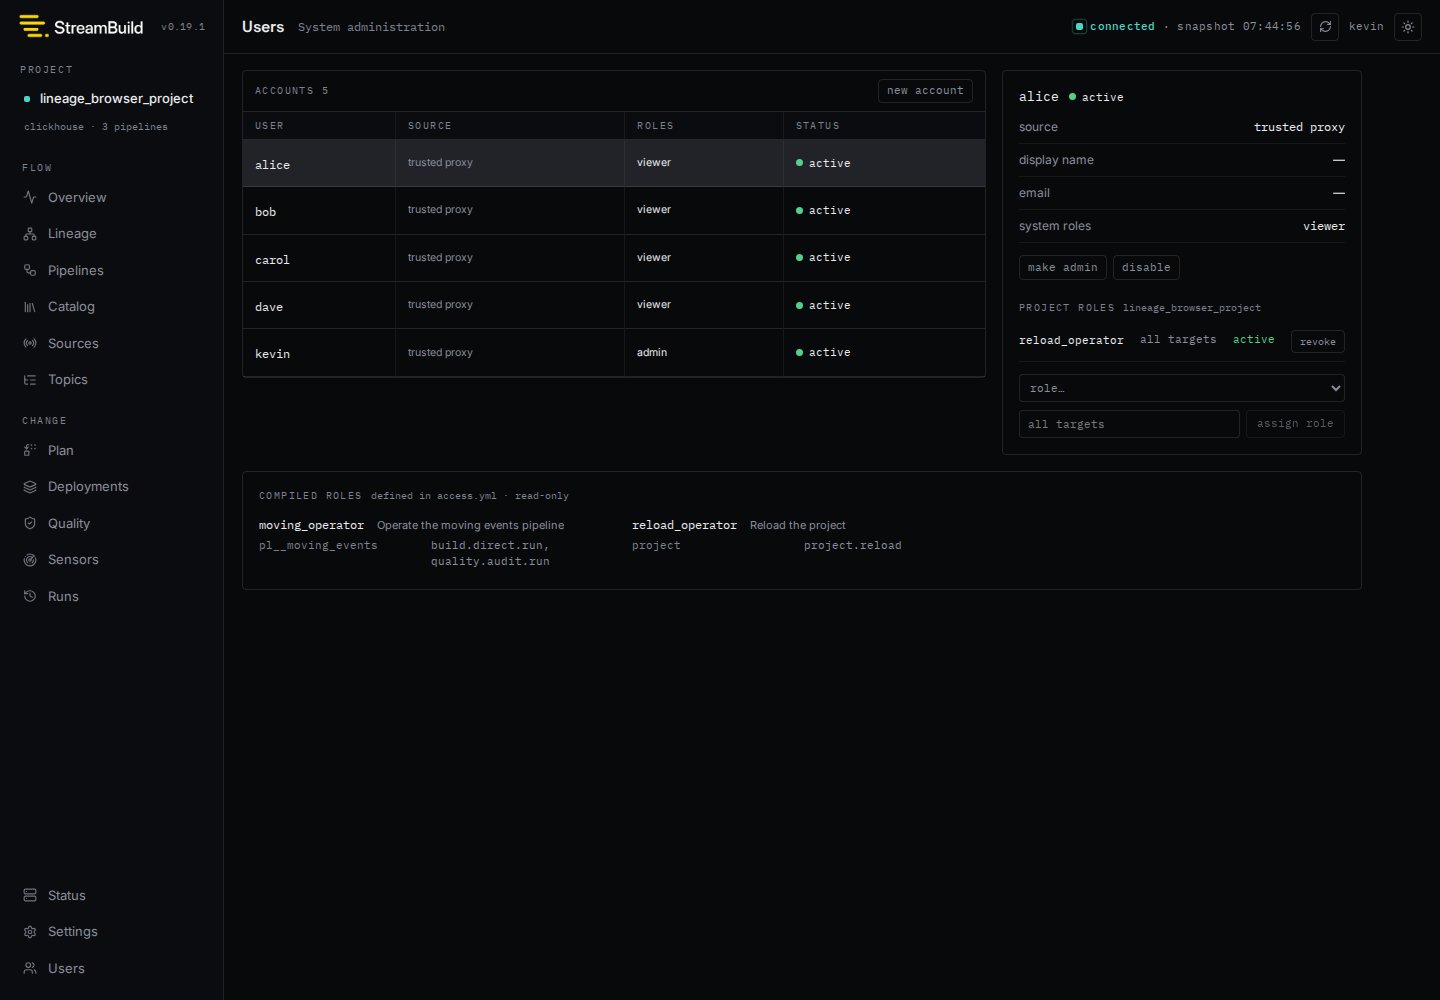
Open Users, select an account, and choose a compiled role. Leave the target empty to assign the role across every target, or enter one target name to constrain it. For example, assign Alice:
The page shows the roles compiled from
access.yml as read-only definitions and lists Alice’s
assignments separately. Assignment changes apply on the next request. If a role is later removed
from access.yml, its assignment is shown as stale and authorizes nothing.
Understand enforcement
The UI disables controls the current user cannot operate, but the API is the security boundary. StreamBuild derives the actual affected pipelines from the compiled plan or warehouse metadata; it does not trust pipeline names supplied by the browser. An operation must be authorized in full. If Alice selectspayments_ingestion and an unauthorized
customer_exports pipeline in one build, StreamBuild rejects the whole request: